 © Fuse Solutions - images digitally composed
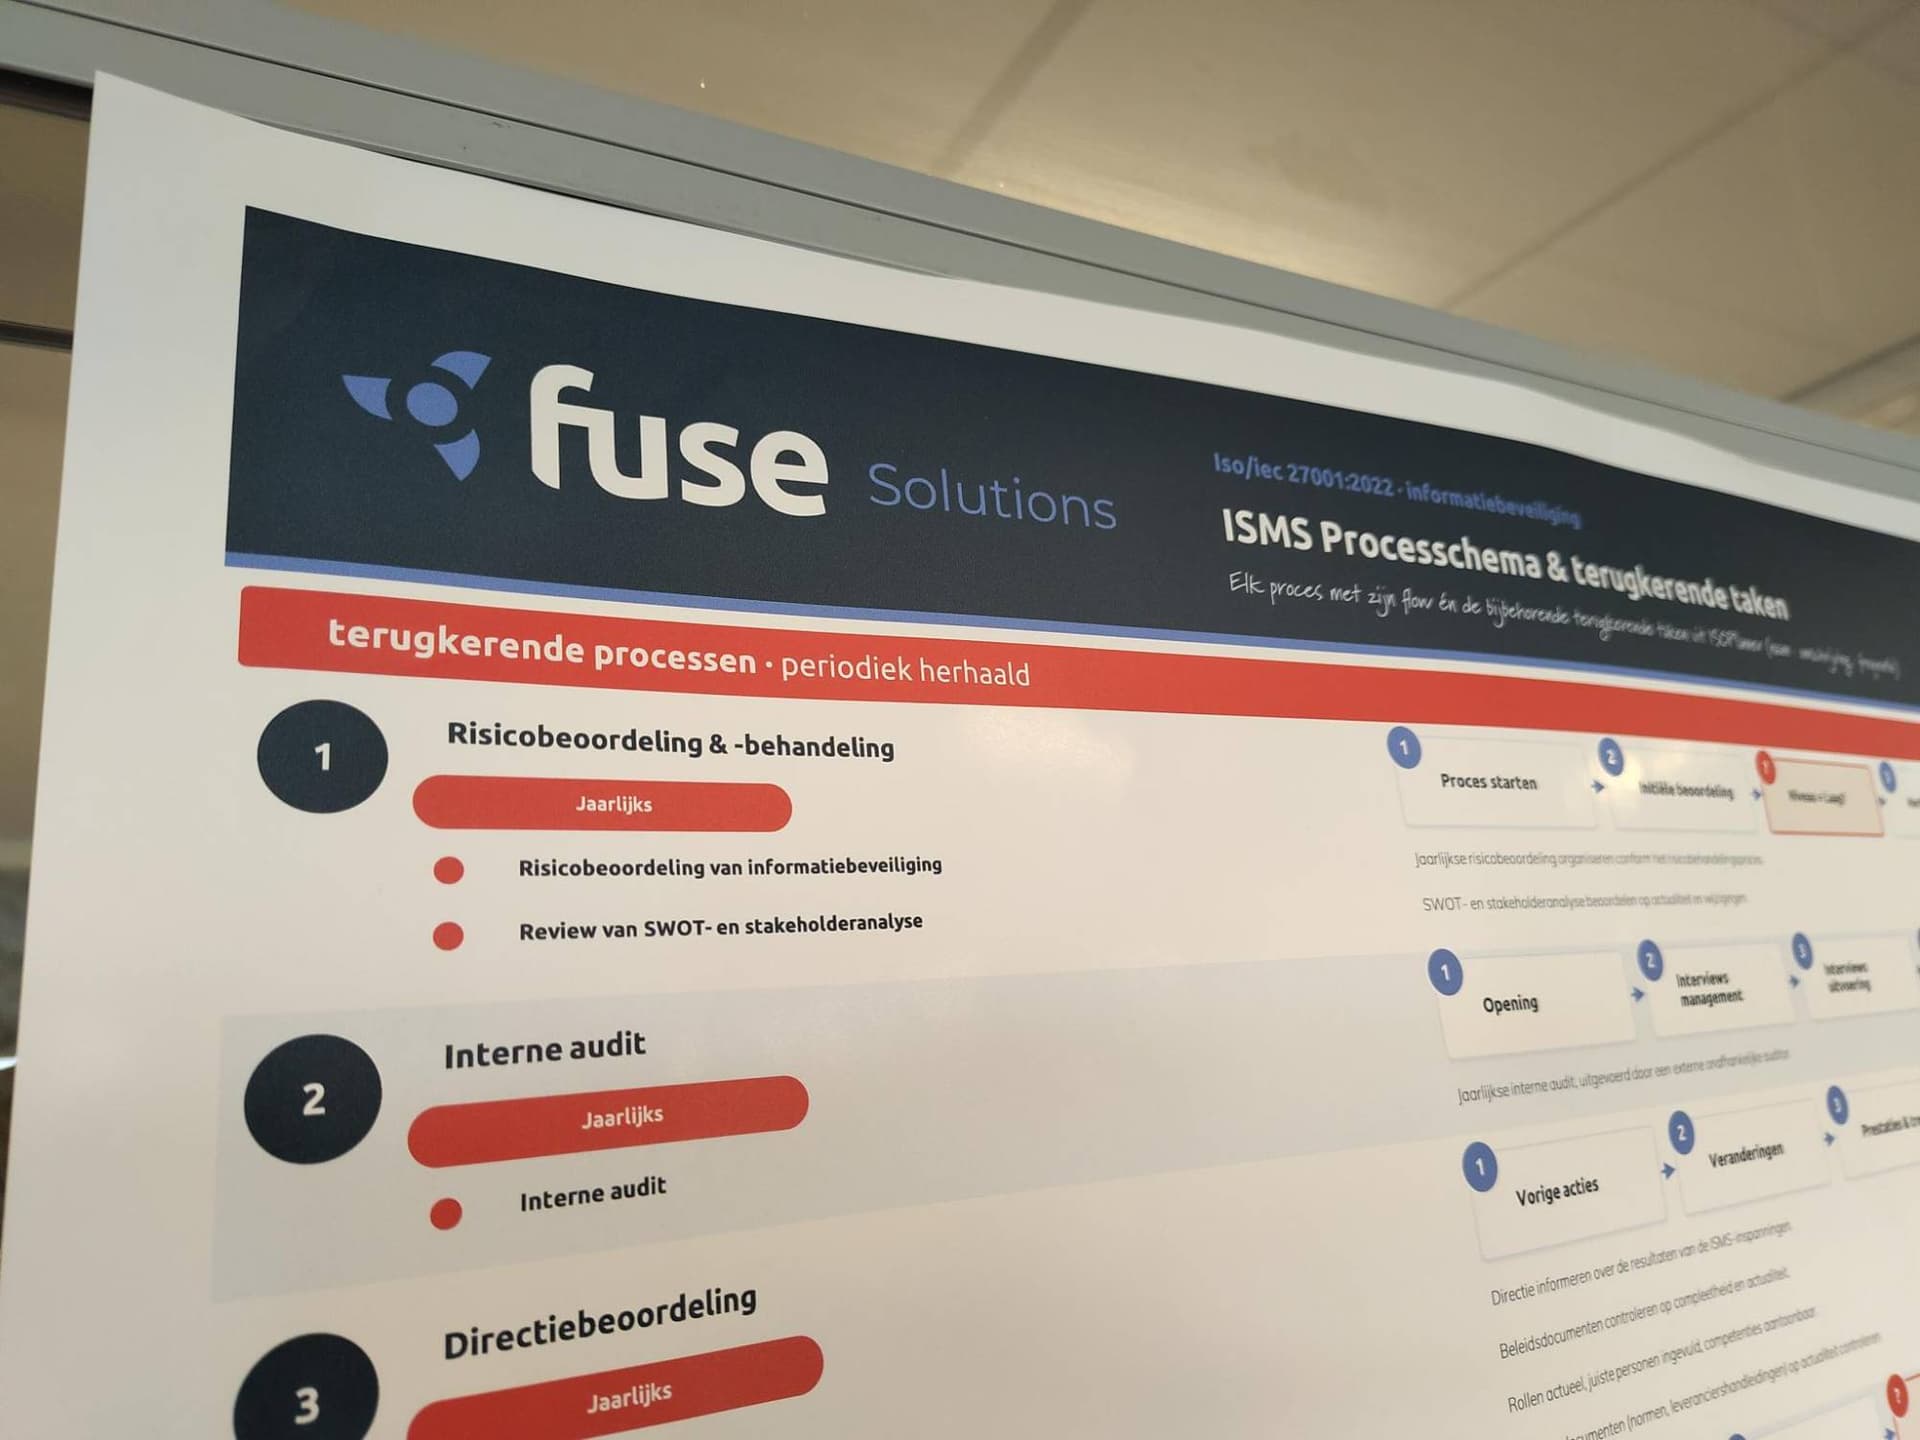
The Fuse Solutions ISMS process diagram: displayed prominently as a poster in our office.
ISO 27001: your project data safe with Fuse after internal audit
Fuse Solutions is in the middle of its ISO 27001 certification process. This summer, we took an important step: we successfully completed the internal audit. The external audit follows in October and November and should lead to the certificate.
Why do we have our data security independently assessed?
Engineers and consultants record their projects, hours, client data and inspection results in our software. That information is often confidential, which is why we have it independently assessed whether it is properly protected. This applies to the complete package in the office, to the Fuse Collect app on site and to the integrations with other systems.
Why ISO 27001 affects your firm too
We see more and more engineering firms exploring an ISO 27001 certificate. The reason is often the same: public sector clients are cautiously starting to ask for it in their tenders. For now, it is usually enough to show that you are working on the implementation. We expect that requirement to become mandatory before long, and that you will need to be certified in about a year.
A process like this also raises the question of how your suppliers handle your data. Your project software holds sensitive information about your clients' projects, including the communication about them. If you work with a supplier that can demonstrate its own information security is in order, that part of your own process is easier to substantiate.
How we safeguard data security
We have firmly embedded data security in our organisation and our software:
- Every client has its own database: environments are fully separated per client, so your data is never mixed with anyone else's
- Relevant Fuse suppliers have been assessed on data security
- Staff work according to fixed, secure protocols
- A hardened login portal protects access to your environment
- Technical and organisational measures have been taken at several levels, including for the integrations with other systems
The ISMS process diagram in the photo hangs in our office. It shows which processes we repeat, such as the risk assessment, the internal audit and the management review. We also test our security frequently and continuously monitor our system for suspicious activity.
Working efficiently on projects, with data that is secure
After the external audit in October and November, we will let you know how the process concluded. To be continued!
Want to know how your firm is doing digitally? The Digital Trust Center of the Dutch Ministry of Economic Affairs helps businesses strengthen their digital resilience. And of course, we are always happy to think along with you when it comes to data security in projects: book an introductory meeting or get in touch with us.
This text was written with the help of AI.